Canberra hit two North Korean shadow financiers and two linked companies with sanctions in late October 2026 over fake IT workers schemes accused of channeling remote tech wages into Pyongyang's nuclear and ballistic missile programs. The move, announced by Foreign Minister Penny Wong on October 23, targeted figures already on Washington's radar—including Sim Hyon Sop and Yu Py Ung—and underlined a harder truth for corporate boards. Remote hiring pipelines built for speed have become an open vault for a sanctioned state.
Sanctions look decisive on a press release. On the ground, they move far slower than a stolen resume.
North Korea's fake IT workers operation is not a handful of rogue freelancers trying to make extra cash. It is a state-directed labor and cyber pipeline designed to extract hard currency from Western firms while keeping operatives out of reach and hidden behind borrowed identities. When Australia moved against key brokers and entities tied to these networks, officials were not just punishing two individuals. They were trying to choke the financial conduits that turn ordinary software paychecks into weapons money.
Why Canberra Targeted the Money Brokers
Surface-level coverage treats sanctions like a courtroom verdict. Someone gets listed, assets get frozen, travel gets blocked, and the story moves on. Anyone who has watched proliferation finance for twenty years knows that is only half the ledger.
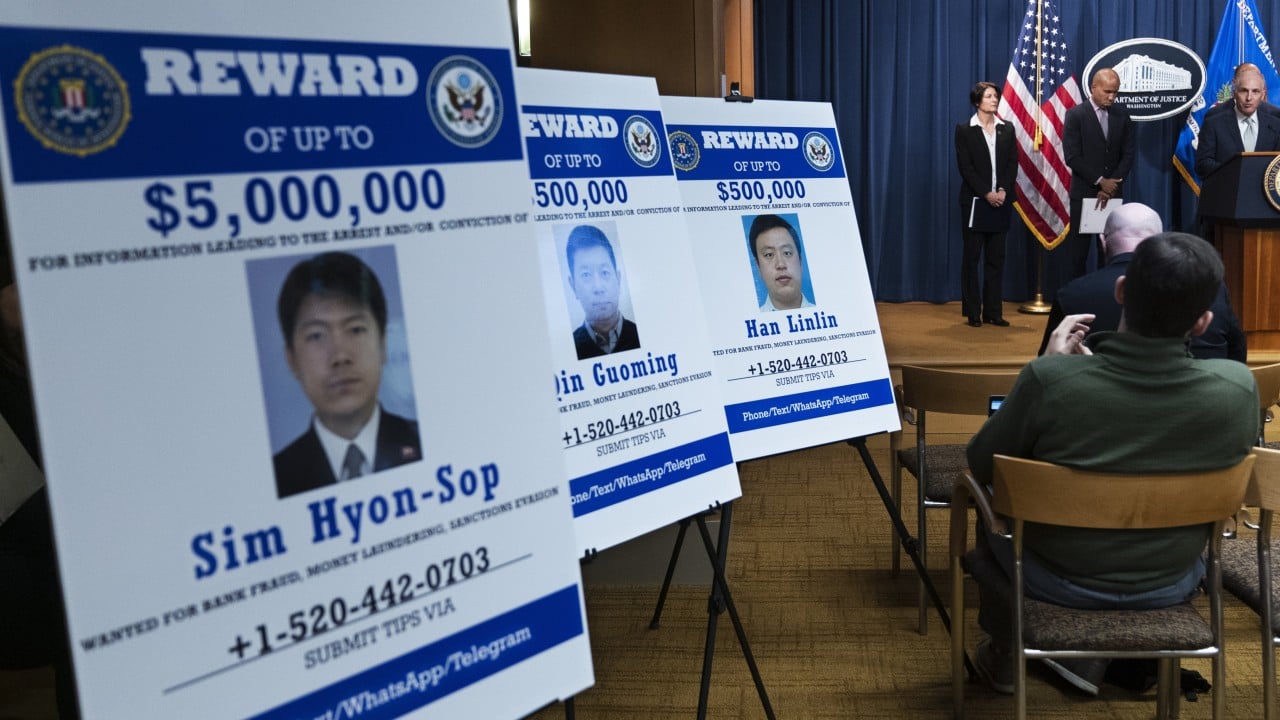
Targeting Sim Hyon Sop and Yu Py Ung alongside two North Korean companies reflects a shift toward financial chokepoints. Sim has long been flagged by US authorities as a major financial broker tied to illicit revenue transfers for Pyongyang, complete with a hefty FBI reward. When states go after facilitators and front companies rather than just low-level coders, they are trying to break the conversion chain—the messy middle where freelance wages, wire transfers, and crypto payouts get bundled and moved back toward regime agencies.
Yet sanctions have a structural blind spot. A sanctioned individual in North Korea or a neighboring jurisdiction rarely holds a clean bank account under their real name in Sydney, London, or New York. They rely on layers of intermediaries, shell structures, cryptocurrency wallets, and compliant or unwitting middlemen. Freezing assets on paper does not automatically stop a contractor in Shenyang, Vladivostok, or Vientiane from logging into a client repository tomorrow morning.
Even so, coordinated pressure still matters. When Australia aligns its listings with US and allied actions, compliance teams at banks, payment processors, and recruiting platforms gain stronger legal footing to reject suspicious payouts and offboard high-risk accounts. It raises friction. Friction is often the best non-kinetic weapon available against a low-cost, high-margin scam.
How the Remote Tech Illusion Works
Most hiring managers assume fraud looks sloppy. Broken English, mismatched time zones, or sketchy portfolios. North Korean IT worker networks succeed because they treat deception like product engineering.
Operatives routinely adopt stolen or fabricated identities belonging to real or plausible foreign nationals, pairing them with AI-generated headshots and polished online footprints to pass initial screening. Video interviews are rehearsed, scripted, or coached. Once an offer lands, the geography trick begins.
Laptop Farms and Proxy Chains
Here is where the scheme gets clever and dangerous. A company ships a corporate laptop to what looks like a domestic address. A local facilitator—sometimes an unwitting accomplice, sometimes a paid insider—receives the machine and plugs it into a laptop farm.
From there, remote-access tools and proxy infrastructure let operatives sitting thousands of miles away control the local hardware. To the employer's endpoint security and IP logs, the employee appears to be sitting in the United States or another approved location. Behind the scenes, teams may share shifts on the same account, producing unnatural login hours or subtle shifts in communication style.
(Note: The following is a hypothetical example illustrating how a typical engagement unfolds.) Imagine a mid-sized software firm hiring a contract backend engineer who claims to live in Chicago. Background checks pass using a compromised identity. The company mails a managed laptop to a residential drop point. Within days, remote access links an operator overseas to that Chicago-based machine. The contractor writes solid code, collects steady biweekly pay, and routes a cut back up the chain—until a security audit notices odd remote-session hops or payroll anomalies.
Beyond Basic Coding Gigs
Early warnings focused heavily on freelance platforms and routine web or mobile development. That picture is outdated.
Government advisories have highlighted operatives branching into fraudulent foreign exchange trading using custom automated systems, as well as pushing for cryptocurrency payments to speed cross-border movement. And the threat is not purely financial. Giving an unverified remote worker privileged access to source code, cloud environments, or internal networks creates an insider risk that traditional perimeter firewalls were never built to stop.
The Uncomfortable Truth About Corporate Hiring
It is easy to blame Pyongyang. Harder to look in the mirror.
During the remote-work boom, many tech firms and agencies compressed hiring cycles to months, weeks, or even days. Distributed teams became a badge of agility. Identity verification often stopped at a quick document scan or a single video call, while contractor onboarding moved faster than security review.
That speed created an attack surface tailor-made for identity fraud. If a company relies on third-party staffing agencies without auditing how those agencies verify candidates, risk gets outsourced right along with the labor. A staffing vendor chasing placement fees has little incentive to slow down a candidate who clears basic checkboxes.
There is also a counter-argument worth taking seriously: aggressive screening can hurt legitimate global talent. Overly rigid geographic rules or blunt automated rejections can lock out honest contractors who simply move frequently, use travel routers, or work irregular hours. Real security requires sharper verification—live liveness checks, multi-stage technical vetting, hardware attestation, and payment controls—not lazy blanket bans that punish innocent workers while clever operators route around them.
What Australian Firms Are Actually Facing
Australian officials have made clear that local companies are not immune. Even when schemes are heavily documented in US investigations, global remote hiring means Australian businesses, startups, and contractors can sit directly in the crosshairs.
For smaller firms without a dedicated counter-proliferation team, the danger is deceptively quiet. There may be no dramatic ransomware note or public breach headline. Instead, there is a slow drain of company funds to a shadow network, or a quietly planted backdoor waiting for a more lucrative moment.
HR, legal, finance, and information security rarely talk enough during contractor hiring. HR cares about filling a seat quickly. Finance cares about paying invoices cleanly. Security cares about access and endpoints. Fake IT worker schemes exploit the gaps between those silos.
Practical Moves Before the Next Hire
Sanctions signal state resolve, but companies carry the front-line responsibility every time they open a requisition for remote talent. Treat every unverified remote contractor as an untrusted endpoint until proven otherwise.
- Tighten identity verification: Pair government ID checks with live video verification, consistent digital history, and cross-checks against red-flag patterns like shifting personas or unusual account sharing.
- Audit staffing intermediaries: Require subcontractors and recruiting partners to prove how they vet candidates, and ban unauthorized sub-outsourcing without written approval.
- Lock down hardware and access: Ship company-managed devices directly to verified employees, monitor for remote-desktop tunneling or anomalous login hours, and enforce least-privilege access from day one.
- Watch the money trail: Flag requests for unusual payment routing, mismatched bank or wallet details, or abrupt shifts in billing jurisdiction.
Every remote hire is now a test of whether your company knows who is actually behind the keyboard.